RCE Vulnerability in React and Next.js

github.com
rce-vulnerability-in-react-and-next.js

A vulnerability affects certain React packages1 for versions 19.0.0, 19.1.0, 19.1.1, and 19.2.0 and frameworks that use the affected packages, including Next.js 15.x and 16.x using the App Router. The issue is tracked upstream as CVE-2025-55182. Fixed in:React: 19.0.1, 19.1.2, … Read more

RCE Vulnerability in QBittorrent

sharpsec.run
rce-vulnerability-in-qbittorrent

In qBittorrent, the DownloadManager class has ignored every SSL certificate validation error that has ever happened, on every platform, for 14 years and 6 months since April 6 2010 with commit 9824d86. The default behaviour changed to verifying on October … Read more

New vulnerability in sha256

github.com
new-vulnerability-in-sha256

{{ message }} This commit does not belong to any branch on this repository, and may belong to a fork outside of the repository. You can’t perform that action at this time.

A Vulnerability in Implementations of SHA-3, Shake, EdDSA

eprint.iacr.org
a-vulnerability-in-implementations-of-sha-3,-shake,-eddsa

Paper 2023/331 A Vulnerability in Implementations of SHA-3, SHAKE, EdDSA, and Other NIST-Approved Algorithm Nicky Mouha, Strativia, Largo, MD, USA Christopher Celi, National Institute of Standards and Technology, Gaithersburg, MD, USA Abstract This paper describes a vulnerability in several implementations … Read more

Vulnerability Management for Go

go.dev
vulnerability-management-for-go

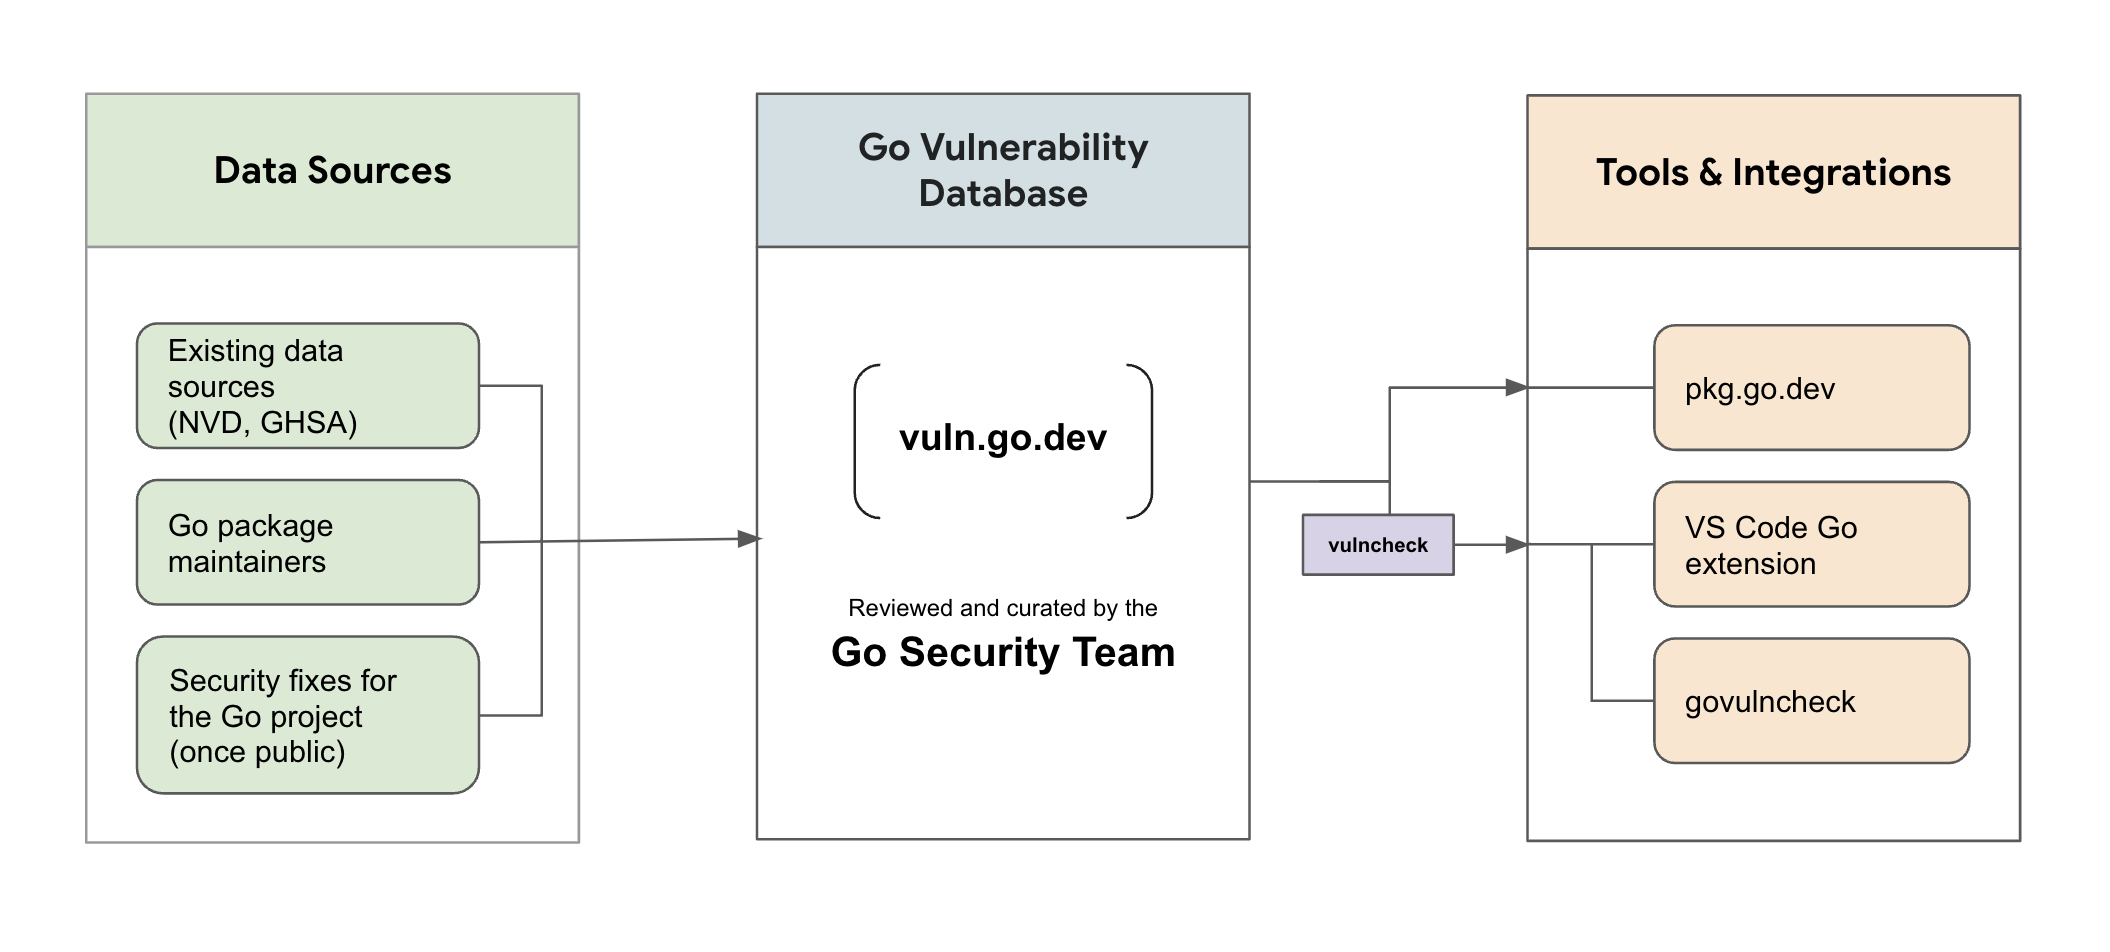
Julie Qiu, for the Go security team6 September 2022 We are excited to announce Go’s new support for vulnerability management, our first step towards helping Go developers learn about known vulnerabilities that may affect them. This post provides an overview … Read more

CVE-2021-44832: New Log4j 2 vulnerability

nvd.nist.gov
cve-2021-44832:-new-log4j-2-vulnerability

CVE-2021-44832 Detail Awaiting Analysis This vulnerability is currently awaiting analysis. Description Apache Log4j2 versions 2.0-beta7 through 2.17.0 (excluding security fix releases 2.3.2 and 2.12.4) are vulnerable to a remote code execution (RCE) attack where an attacker with permission to modify … Read more

0-Day Vulnerability on Log4j

blog.sonatype.com
0-day-vulnerability-on-log4j

News broke early Friday morning of a serious 0-day Remote Code Execution exploit in log4j – CVE-2021-44228– the most popular java logging framework used by Java software far and wide. This type of vulnerability is especially dangerous as it can … Read more