
Detecting the use of “curl | bash” server side (2016)
idontplaydarts.com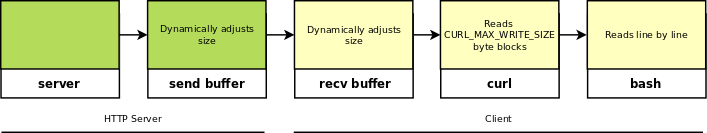
Installing software by piping from curl to bash is obviously a bad idea and a knowledgable user will most likely check the content first. So wouldn’t it be great if a malicious payload would only render when piped to bash? … Read more

