Let’s Talk about PAKE

blog.cryptographyengineering.com
let’s-talk-about-pake

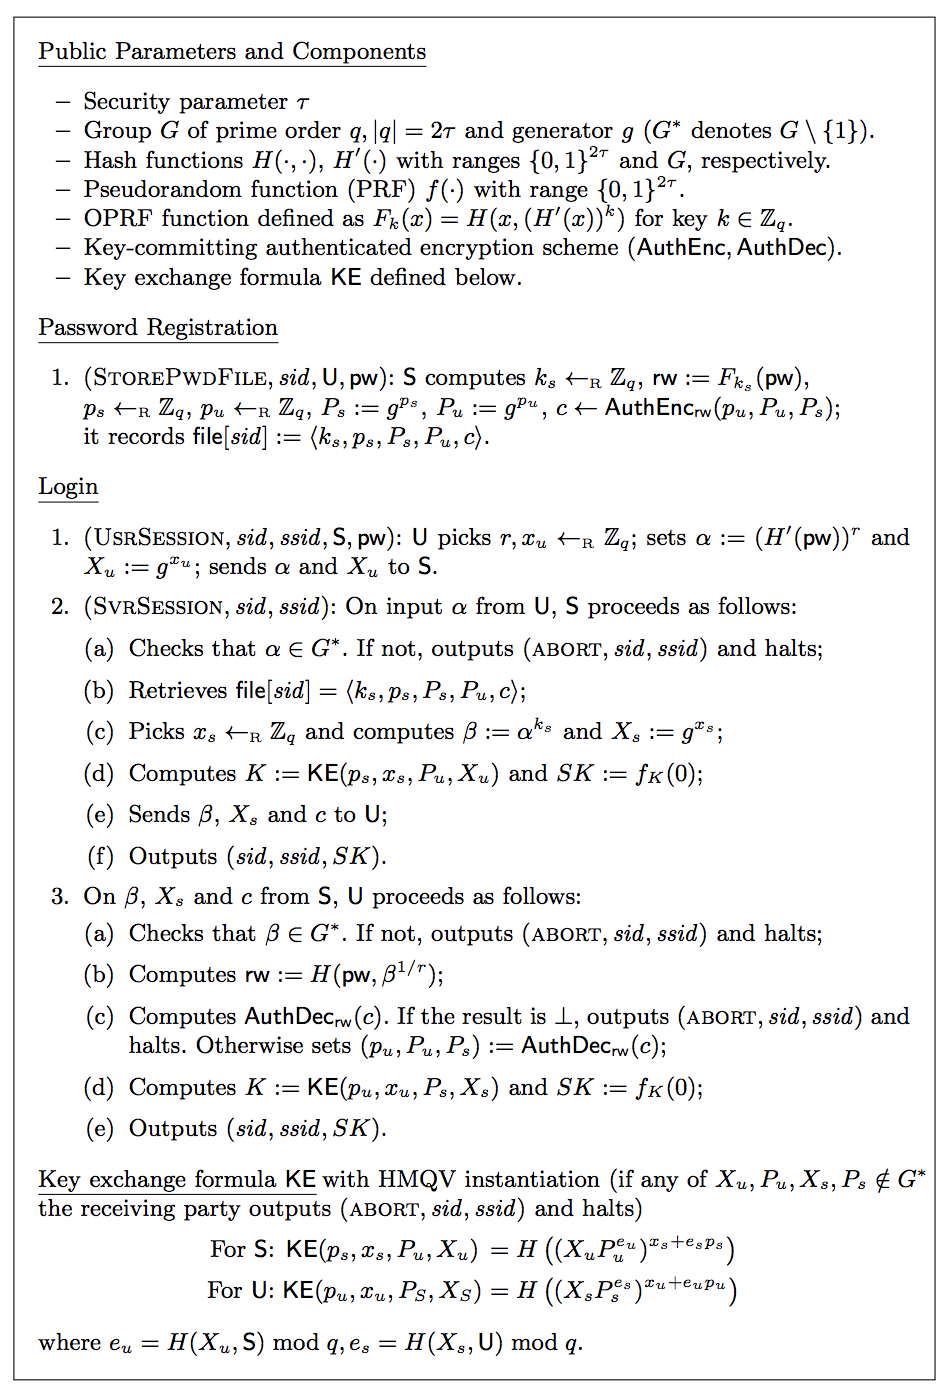
The first rule of PAKE is: nobody ever wants to talk about PAKE. The second rule of PAKE is that this is a shame, because PAKE — which stands for Password Authenticated Key Exchange — is actually one of the most useful … Read more
Thinking about “traceability” (Matthew Green)

blog.cryptographyengineering.com
thinking-about-“traceability”-(matthew-green)

A few weeks ago the messaging service WhatsApp sued the Indian government over new legislation that could undermine its end-to-end encryption (E2EE) software. The legislation requires, among other things, that social media and messaging companies must include the ability to … Read more

A case against security nihilism

blog.cryptographyengineering.com
a-case-against-security-nihilism

This week a group of global newspapers is running a series of articles detailing abuses of NSO Group’s Pegasus spyware. If you haven’t seen any of these articles, they’re worth reading — and likely will continue to be so as … Read more