Writing a system call tracer using eBPF
sh4dy.com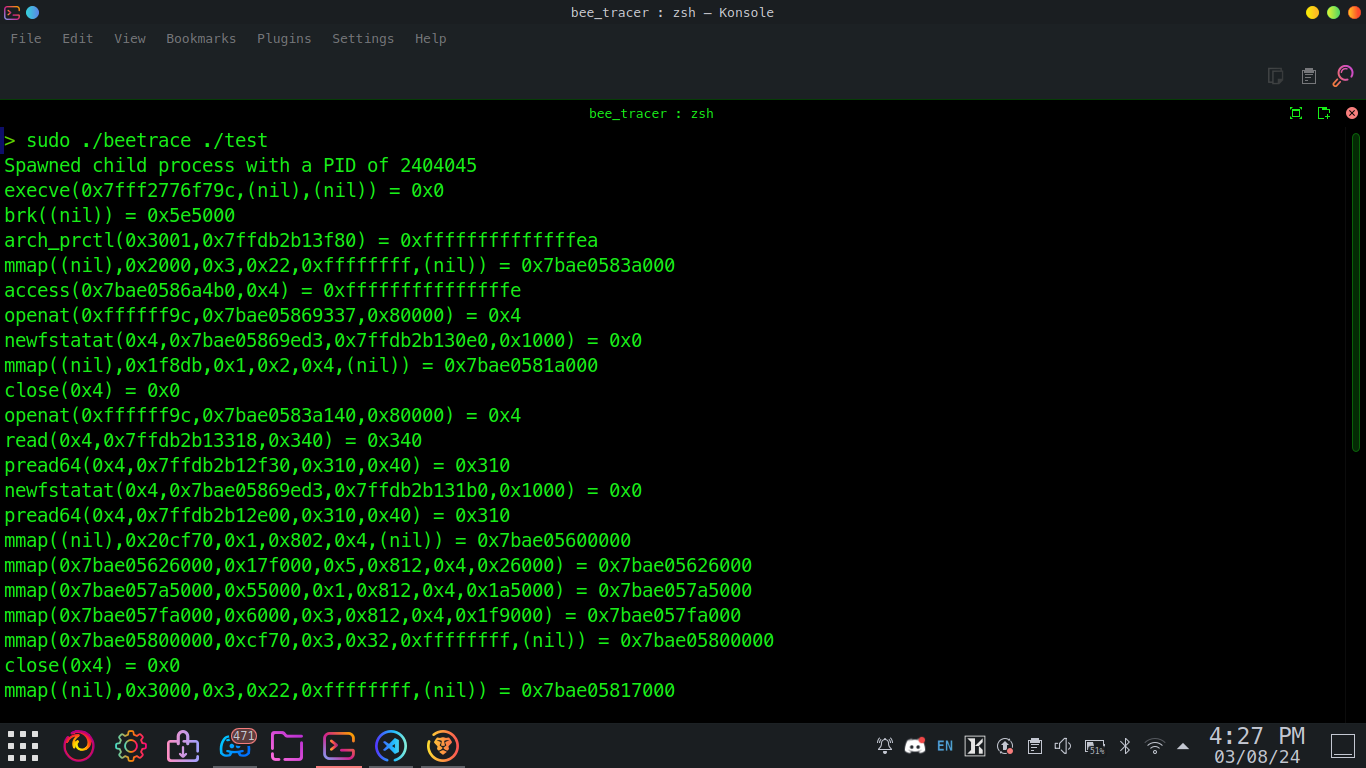
Pre-Requisites System calls, eBPF, C, basics of low-level programming. Introduction eBPF (Extended Berkeley Packet Filter) is a technology that allows users to run custom programs within the kernel. BPF / or cBPF (classic BPF), the predecessor of eBPF provided a … Read more